
Loading, please wait...
Loading, please wait...
iRhythm Holdings recently reported a significant security event involving unauthorized activity on certain third-party applications. Consequently, healthcare providers are closely monitoring this iRhythm cybersecurity incident to understand its impact on clinical services. Fortunately, the medtech firm confirmed that the breach did not affect its core medical products or patient care systems.
The company first detected unusual activity on June 8, 2026. Therefore, they immediately launched an investigation alongside external cybersecurity experts. The next day, a threat actor claimed to possess sensitive proprietary information and patient protected health information. Although the hackers demanded a ransom payment, iRhythm took immediate containment measures. Specifically, the affected data resided solely on third-party-hosted business systems rather than clinical networks.
Most importantly, the cyber threat did not impact patient safety. iRhythm clarified that its clinical monitoring systems and medical devices remain fully secure. Furthermore, the company does not store individual financial account or payment card information on these servers. Thus, manufacturing and distribution operations are continuing without any interruption. Doctors can safely continue using these cardiac monitors for their patients.
Q1: Was patient safety affected by this security breach?
No, patient safety remains unaffected because the incident did not involve any clinical or medical device systems.
Q2: What type of data did the threat actors target?
The threat actors targeted data on certain third-party-hosted business applications through social engineering, which may include some patient protected health information.
Disclaimer: This content is for informational and educational purposes only. It does not constitute medical advice or replace professional judgment. Refer to the latest local and national guidelines for clinical practice.
References
Read summarized clinical updates, watch expert medical content, and earn CME certifications right from your smartphone.
Open your smartphone camera to scan and install.
Medical device maker iRhythm Holdings recently experienced a cybersecurity incident involving third-party applications. Although the threat actor claims to hold patient protected health information, the company has confirmed that its clinical systems, patient safety, and medical devices remain completely unaffected.
4 months ago
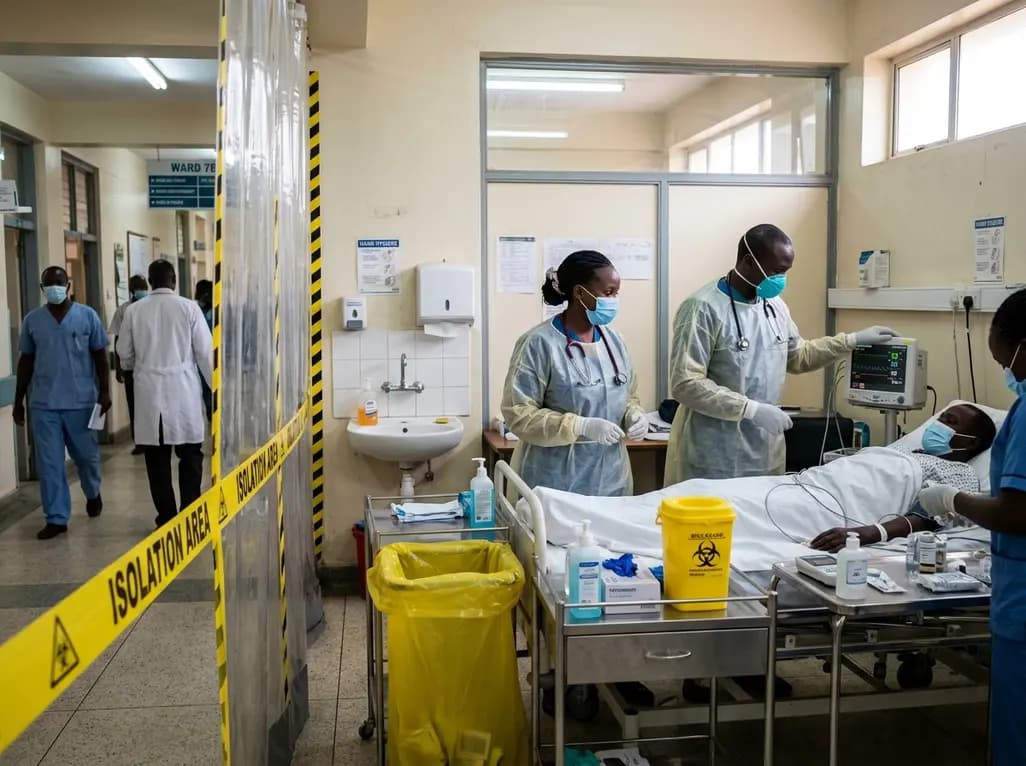
Kenya's confirmation of its eighth Ebola infection highlights the acute risk of secondary transmission in hospital environments. Clinicians must maintain high vigilance, enforce strict infection prevention protocols, and implement rapid triage mechanisms for viral hemorrhagic fevers across healthcare settings.
4 days back
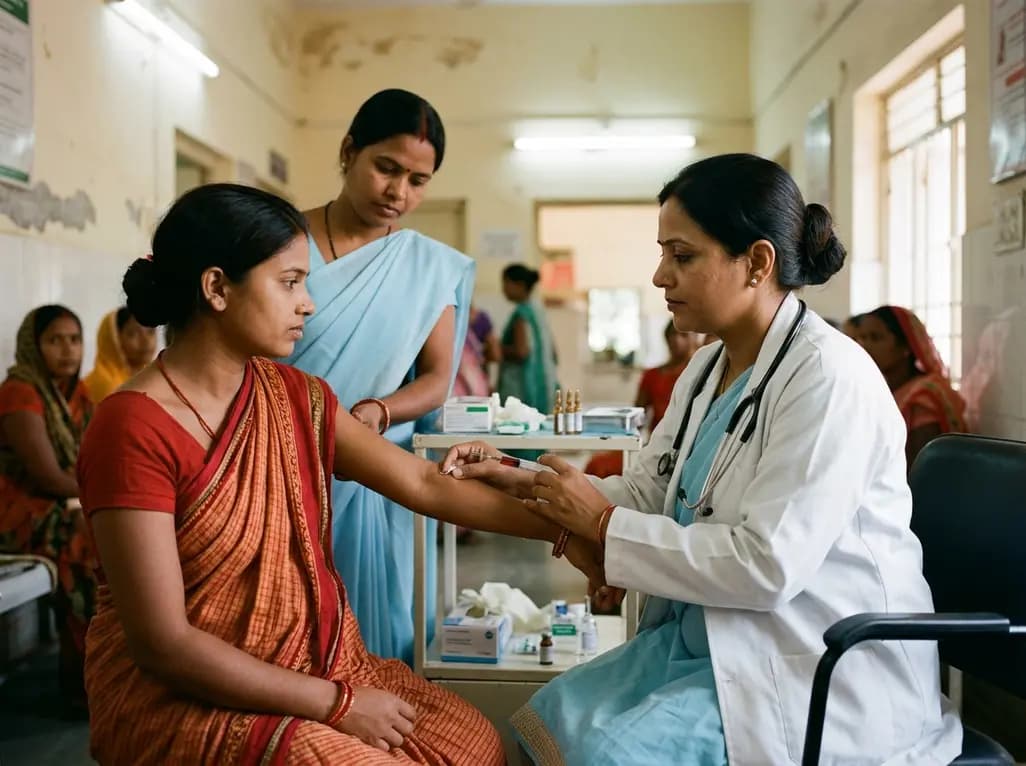
Maternal anaemia contributes to nearly half of pregnancy-related fatalities across India. To prevent complications, Uttar Pradesh has added single-dose parenteral iron to its essential medicines list. This clinical transition aims to restore haemoglobin rapidly and protect high-risk mothers across rural facilities.
Last week
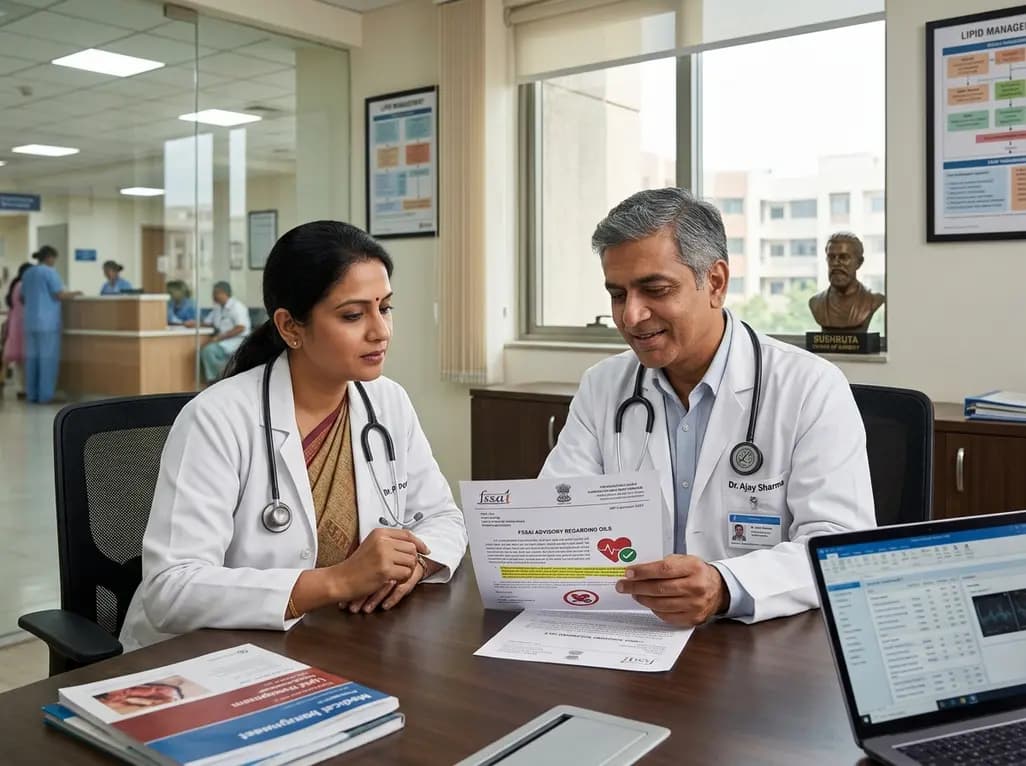
India's food safety authority FSSAI has issued show-cause notices to Gemini Edibles, BigBasket, and Flipkart for unpermitted cardiovascular claims regarding Freedom Rice Bran Oil. This regulatory move highlights the strict enforcement of advertising standards and the clinical necessity of evidence-based lipid care.
6 days back
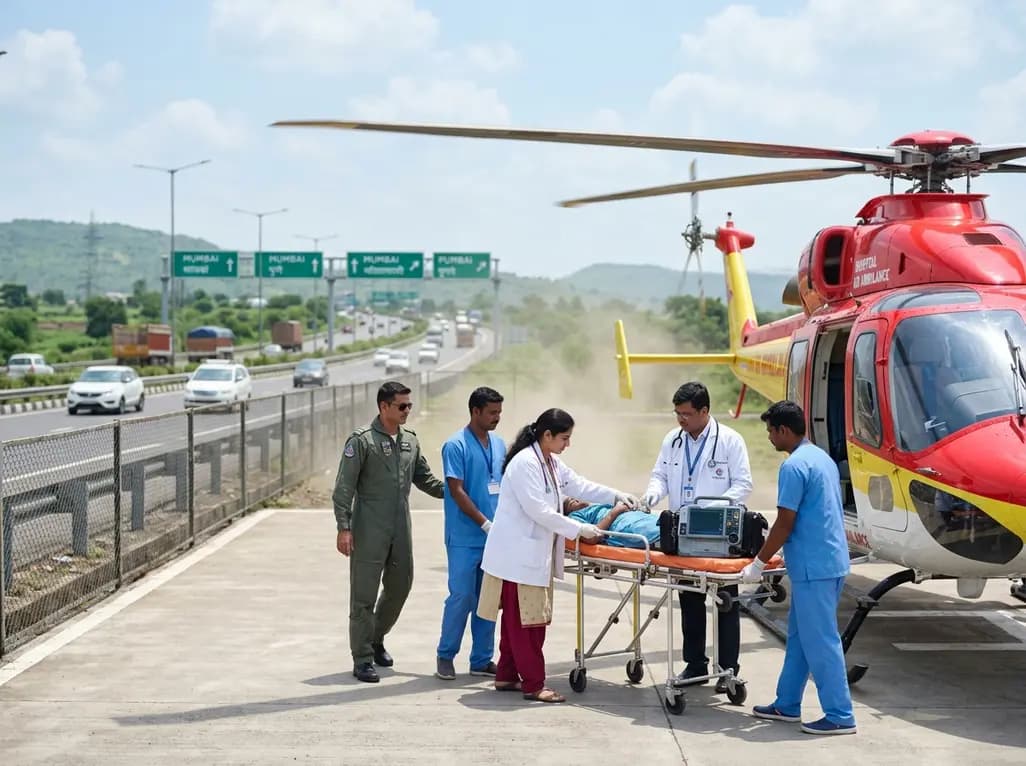
The state government is deploying helicopter emergency medical services across the Mumbai-Pune Expressway, Samruddhi Mahamarg, and Mumbai-Goa Highway. This initiative establishes unified standard operating procedures to enable rapid triage, advanced prehospital resuscitation, and seamless trauma care transfers.
Last week
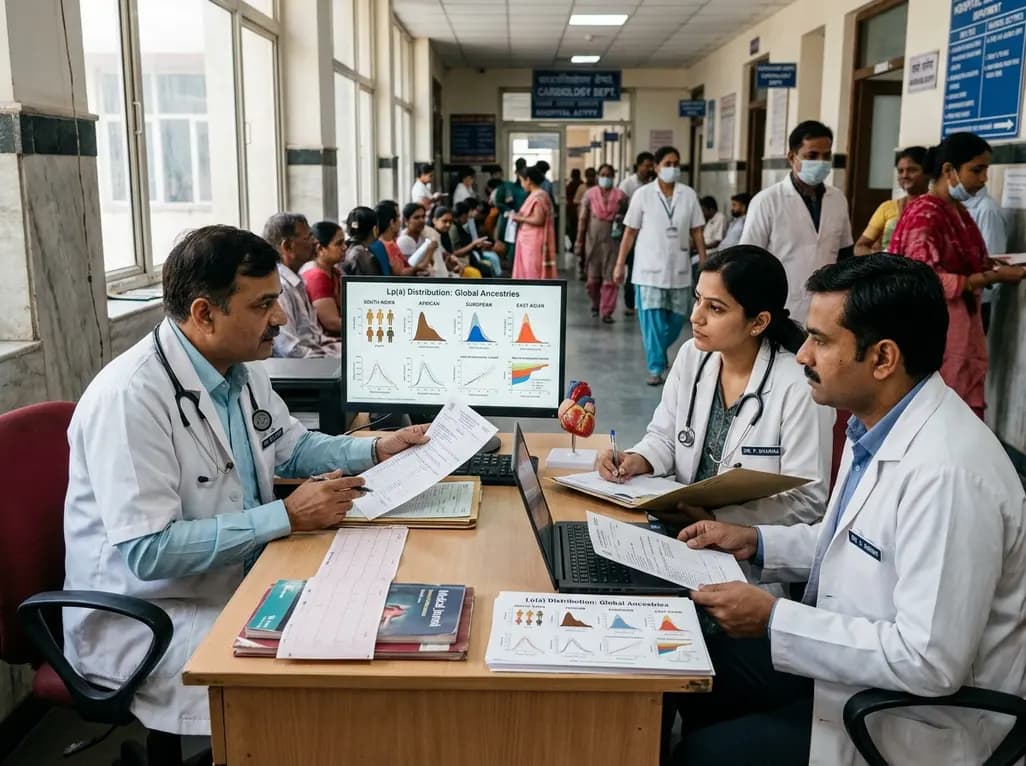
Atherosclerotic cardiovascular disease guidelines often rely on European-derived lipoprotein(a) cutoffs. However, baseline Lp(a) levels vary widely across ancestries, including South Asians and Africans. Clinicians must interpret Lp(a) values within overall absolute cardiovascular risk.
Last week